Your guiding light through digital risk
Leadership that sees what’s coming.
Fractional executives and risk programs for mid-market businesses. One accountable owner for digital risk, sized to how your business actually runs.
When firms call us
The moments that force change.
Cyber, technology, AI, and resilience used to sit in separate lanes. Boards, regulators, clients, and insurers now ask one question across all of them: who owns the risk?
- A board asking who’s accountable for cyber, AI, and technology risk
- AI already in use across the business, with no policy and no owner
- A client or regulator questionnaire you can’t answer cleanly
- A recovery plan that’s never been tested against a real outage
- An audit finding or insurance renewal with no one to own it
- A CISO, CIO, or risk seat sitting empty
Two ways we work
One continuum.
Fractional Leadership
CISO · CIO / CTO · CRO
A senior executive in your security, technology, or risk seat, part-time. We own the strategy and the program, and we’re the accountable voice with your board and clients.
Explore fractional leadership →
Digital Risk Programs
Resilience · AI governance · GRC
Defined-scope builds: disaster recovery and operational resilience, AI governance, framework readiness (ISO 27001, ISO 42001, SOC 2, and more), SDLC governance, audit response and remediation.
Explore digital risk programs →Most engagements start with one and grow into the other.
How we’re different
“We don’t sell the easy button.”
We step into the executive seat and build the governance and resilience programs underneath it. That means diagnosing what’s actually broken beneath the surface findings, building for how you actually operate, and staying on watch long after the deliverable.
The whole picture
We diagnose what’s actually broken beneath the surface findings.
On watch
Still here long after the deliverable, through renewals, audits, and whatever comes next.
No easy button
Real programs built for how you actually operate, not shortcuts built for the binder.
Who you’ll work with
The principal leads every engagement.
Dan Gorecki brings twenty-plus years across CIO, CISO, and risk leadership, from 30-person startups to a Fortune 200. Senior advisors with the same operator background join when the work needs more hands.
Meet the team →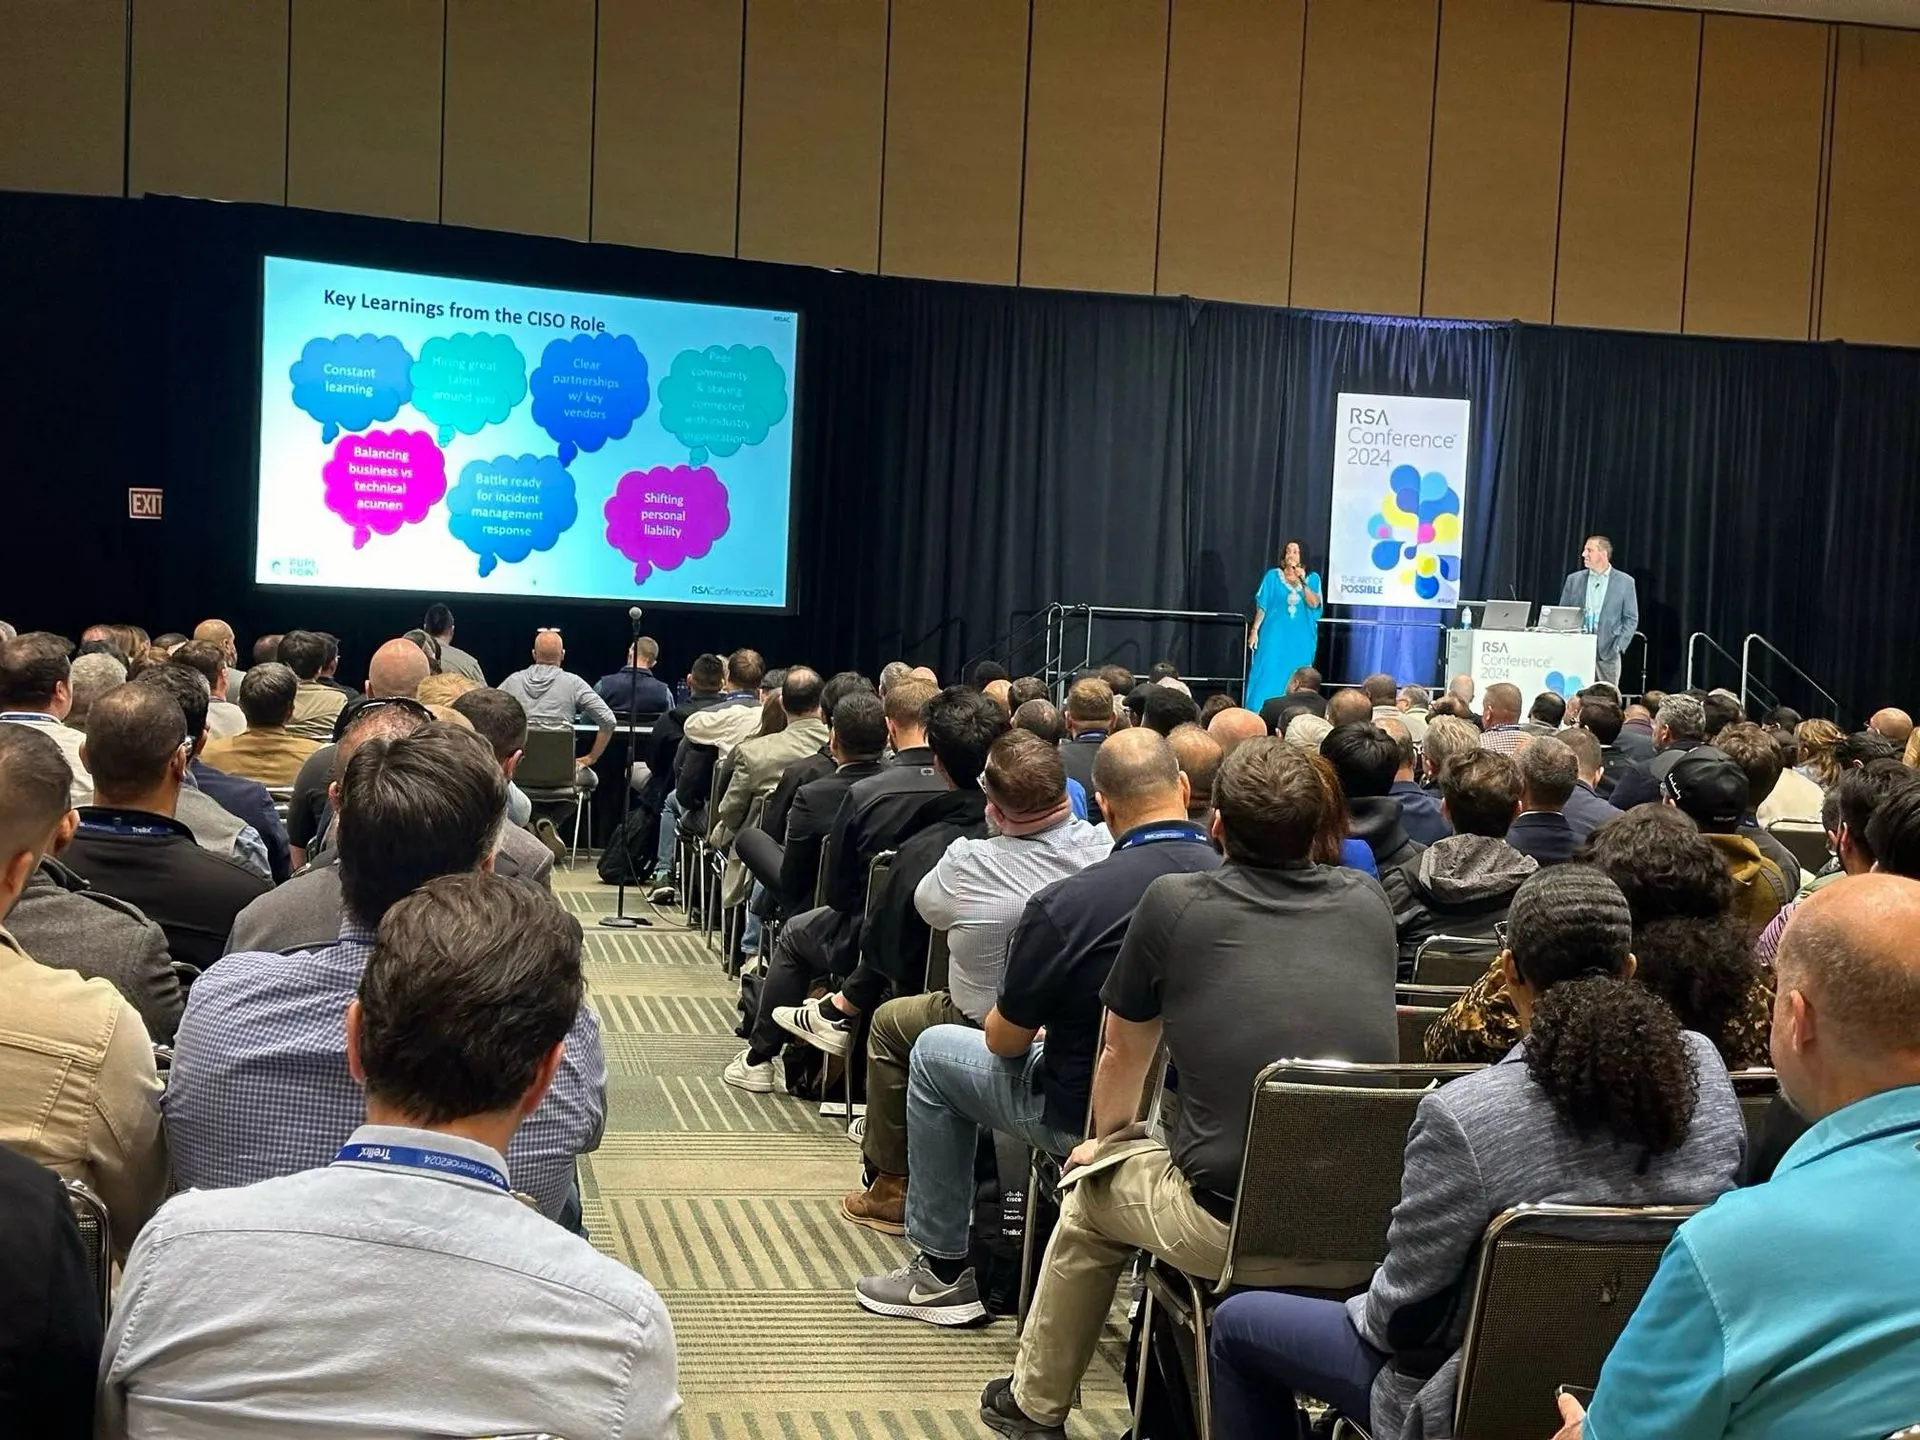
Speaking & community
In the room where the profession is shaped.
Co-chair of RSAC’s CISO Boot Camp for 2027 and SIM’s DigiRisk special interest group, and a regular voice at conferences, panels, and podcasts.
Speaking & media →From NGC Risk
The Wardroom
An enterprise risk reasoning platform, now in closed beta.
Start a conversation
Let’s talk about what’s coming.
Tell us what’s prompting the call: a board question, an AI rollout, an audit finding, or an empty seat. We’ll take it from there.